Blog
Upwind Blog
Feed
Grid
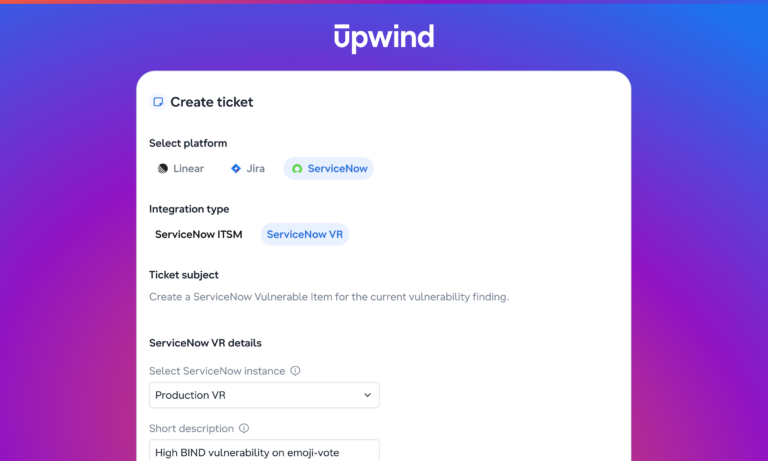
Upwind + ServiceNow VR: Only real findings reach the ticket queue

Send vulnerability findings straight into your VR queues, and let Upwind verify every fix before a ticket stays closed. Key Takeaways Upwind now integrates with ServiceNow Vulnerability Response (VR), the ServiceNow module where remediation teams track and fix vulnerabilities. The integration is generally available. It sends Upwind findings into VR as native Vulnerable Items and…
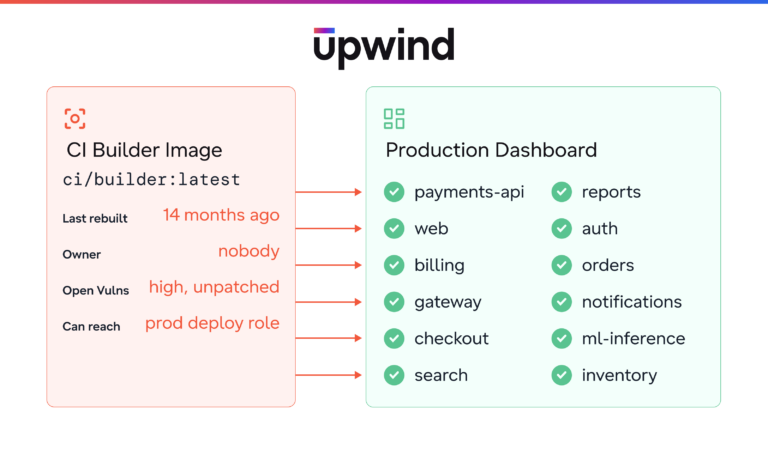
Your CI Runner Image Can Deploy to Prod. Who’s Scanning It?

How to find, rank, and trace the most privileged containers in your cloud before an attacker does Key Takeaways Every recent supply-chain attacks hit the build path Someone reports a compromise in a popular CI dependency, and security asks one question in the incident channel: "Are we affected?" Production dashboards are green, runtime alerts are…
Kick the Bucket: S3 Bucket Squatting Through a Series of Half-Patched AWS Patterns

This is the fourth and final post in our series on S3 bucket squatting in AWS. In the three preceding posts, we walked through the individual findings: cross-tenant RCE in SageMaker, silent query exfiltration in Athena, and log capture in EMR. Here we step back to share how we found them, why the fixes failed,…
Spark in the Dark: Silent Cross-Tenant Log Exfiltration in Amazon EMR
This is the third post in our series on S3 bucket squatting through half-patched AWS patterns. Previously, we covered cross-tenant RCE in SageMaker via a broken ownership check and silent query result exfiltration in Athena through an SDK that was never patched alongside the service. This time, we cover an actively exploitable vulnerability in EMR.…
Athena’s Trojan Horse: Cross-Tenant Data Poisoning and Exfiltration via AWS Athena
This is the second post in our series on S3 bucket squatting vulnerabilities that survived AWS remediation. In the first post, we showed how a logic bug in the SageMaker Python SDK's ownership check enabled cross-tenant RCE on live ML pipelines. Here we turn to Athena, where a gap between the service-level fix and the…
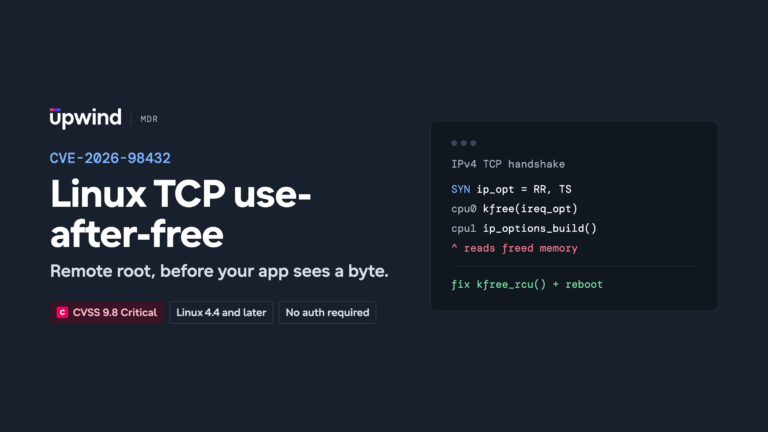
CVE-2026-98432: Inside the Critical Linux TCP Use-After-Free That Fires Before Your App Sees a Byte
A use-after-free in the Linux kernel's IPv4 TCP handshake (CVE-2026-98432, CVSS 9.8) was fixed upstream in October and is still landing in distribution kernels. What we found: any unauthenticated peer can reach it on any IPv4 TCP port; the working root exploit has been described but not published; and the setup it needs is more…
Training on Enemy Ground: Cross-Tenant RCE in Amazon SageMaker
This is the first in a four-part series on S3 bucket squatting vulnerabilities we found across AWS services, each in a service that had already been "fixed." We start with the most severe: cross-tenant remote code execution in Amazon SageMaker. TL;DR We found that AWS SageMaker's default S3 bucket - used by virtually every SageMaker…
The Next Wave Is Here: Upwind’s $400M Series C to Build The Cloud & AI Security Platform

Today, we are marking an important milestone in our incredible journey. Less than 9 months since we announced our $250M Series B, we are thrilled to announce our $400M Series C funding led by Bessemer Venture Partners with participation from each and every Upwind's investor: Greylock Partners, Cyberstarts, Craft, Salesforce Ventures, Alta Park, Picture Capital,…
PHP2Shell: Inside the Two Critical PHP RCE Flaws

Two critical remote-code-execution flaws in PHP (CVE-2026-109618 and CVE-2026-109619) were patched on 21 October 2026. What we found: the public "php2shell" exploit targets the wrong bug, the real flaw is engine-wide, and the loud "the patch is already broken" claims do not hold up. TL;DR On 21 October 2026 the PHP project shipped emergency fixes…
LiteLLM 1.107.0 Supply Chain Attack: How a Hijacked Release Pipeline Signed Malicious Code
TL;DR On October 21, 2026, Upwind identified a supply chain compromise in LiteLLM, the popular open-source AI gateway, with ~22.8 million weekly PyPI downloads. Version 1.107.0 was published to PyPI and to Docker Hub/GHCR containing a credential stealer and a remote code loader. We were the first to report it publicly, in BerriAI/litellm#47826 and on…
HTTP2Shell (CVE-2026-111497): one Brotli bug, RCE across the HTTP stack
TL;DR HTTP2Shell (CVE-2026-111497) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0. An unauthenticated attacker who gets crafted Brotli data into a vulnerable decoder can crash the process, read its memory, or in some cases run code. It was first reported as a Node.js bug ("Node2Shell"), but the flaw is in the…
The context gap: what runtime context changes in cloud and AI security


Key takeaways Most cloud security teams can see their environment. Inventory is broad, scanners run on schedule and findings pile up. What they can't tell you is which of those findings matter right now. That's the context gap. Visibility was the right foundation, and most programs have built it (see where yours sits on the…
The Next Wave Is Here: Upwind’s $400M Series C to Build The Cloud & AI Security Platform
Today, we are marking an important milestone in our incredible journey. Less than 9 months since we announced our $250M Series B, we are thrilled to announce our $400M Series C funding led by Bessemer Venture Partners with participation from each and every Upwind's investor: Greylock Partners, Cyberstarts, Craft, Salesforce Ventures, Alta Park, Picture Capital,…
Latest
November 4, 2026
Upwind + ServiceNow VR: Only real findings reach the ticket queue
Send vulnerability findings straight into your VR queues, and let Upwind verify every fix before a ticket stays closed. Key Takeaways Upwind now integrates with ServiceNow Vulnerability Response (VR), the ServiceNow module where remediation teams track and fix vulnerabilities. The integration is generally available. It sends Upwind findings into VR as native Vulnerable Items and…
November 3, 2026
Your CI Runner Image Can Deploy to Prod. Who’s Scanning It?
How to find, rank, and trace the most privileged containers in your cloud before an attacker does Key Takeaways Every recent supply-chain attacks hit the build path Someone reports a compromise in a popular CI dependency, and security asks one question in the incident channel: "Are we affected?" Production dashboards are green, runtime alerts are…
November 2, 2026
Kick the Bucket: S3 Bucket Squatting Through a Series of Half-Patched AWS Patterns
This is the fourth and final post in our series on S3 bucket squatting in AWS. In the three preceding posts, we walked through the individual findings: cross-tenant RCE in SageMaker, silent query exfiltration in Athena, and log capture in EMR. Here we step back to share how we found them, why the fixes failed,…
November 2, 2026
Spark in the Dark: Silent Cross-Tenant Log Exfiltration in Amazon EMR
This is the third post in our series on S3 bucket squatting through half-patched AWS patterns. Previously, we covered cross-tenant RCE in SageMaker via a broken ownership check and silent query result exfiltration in Athena through an SDK that was never patched alongside the service. This time, we cover an actively exploitable vulnerability in EMR.…
November 2, 2026
Athena’s Trojan Horse: Cross-Tenant Data Poisoning and Exfiltration via AWS Athena
This is the second post in our series on S3 bucket squatting vulnerabilities that survived AWS remediation. In the first post, we showed how a logic bug in the SageMaker Python SDK's ownership check enabled cross-tenant RCE on live ML pipelines. Here we turn to Athena, where a gap between the service-level fix and the…
November 2, 2026
CVE-2026-98432: Inside the Critical Linux TCP Use-After-Free That Fires Before Your App Sees a Byte
A use-after-free in the Linux kernel's IPv4 TCP handshake (CVE-2026-98432, CVSS 9.8) was fixed upstream in October and is still landing in distribution kernels. What we found: any unauthenticated peer can reach it on any IPv4 TCP port; the working root exploit has been described but not published; and the setup it needs is more…
November 2, 2026
Training on Enemy Ground: Cross-Tenant RCE in Amazon SageMaker
This is the first in a four-part series on S3 bucket squatting vulnerabilities we found across AWS services, each in a service that had already been "fixed." We start with the most severe: cross-tenant remote code execution in Amazon SageMaker. TL;DR We found that AWS SageMaker's default S3 bucket - used by virtually every SageMaker…
October 26, 2026
PHP2Shell: Inside the Two Critical PHP RCE Flaws
Two critical remote-code-execution flaws in PHP (CVE-2026-109618 and CVE-2026-109619) were patched on 21 October 2026. What we found: the public "php2shell" exploit targets the wrong bug, the real flaw is engine-wide, and the loud "the patch is already broken" claims do not hold up. TL;DR On 21 October 2026 the PHP project shipped emergency fixes…
October 26, 2026
LiteLLM 1.107.0 Supply Chain Attack: How a Hijacked Release Pipeline Signed Malicious Code
TL;DR On October 21, 2026, Upwind identified a supply chain compromise in LiteLLM, the popular open-source AI gateway, with ~22.8 million weekly PyPI downloads. Version 1.107.0 was published to PyPI and to Docker Hub/GHCR containing a credential stealer and a remote code loader. We were the first to report it publicly, in BerriAI/litellm#47826 and on…
October 24, 2026
HTTP2Shell (CVE-2026-111497): one Brotli bug, RCE across the HTTP stack
TL;DR HTTP2Shell (CVE-2026-111497) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0. An unauthenticated attacker who gets crafted Brotli data into a vulnerable decoder can crash the process, read its memory, or in some cases run code. It was first reported as a Node.js bug ("Node2Shell"), but the flaw is in the…
October 22, 2026
The context gap: what runtime context changes in cloud and AI security
Key takeaways Most cloud security teams can see their environment. Inventory is broad, scanners run on schedule and findings pile up. What they can't tell you is which of those findings matter right now. That's the context gap. Visibility was the right foundation, and most programs have built it (see where yours sits on the…
October 21, 2026
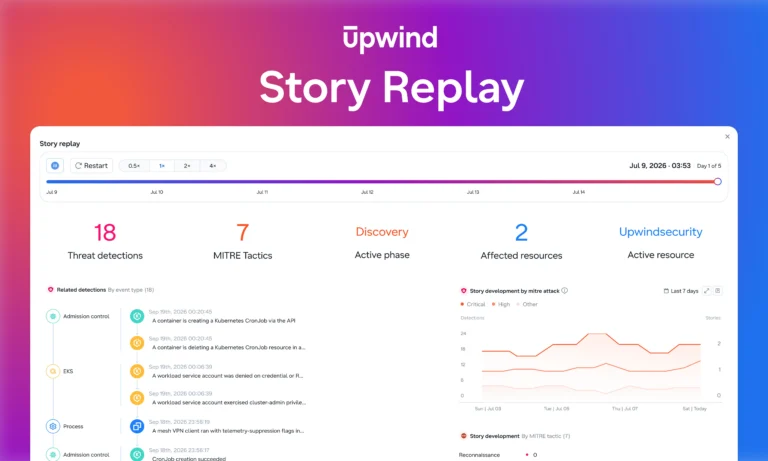
Upwind Story Replay: Watch the Attack Unfold

Upwind Story Replay is now available in Upwind: a visual timeline of the detections that led to a threat. Click a threat story, watch the attack unfold step by step. Three Vectors in One Week AI is accelerating everything we knew about supply chain attacks, zero-days, and finding new critical CVEs. Attacks are unfolding fast…